«أنثروبيك» تحذر من اقتراب قدرة نماذج الذكاء الاصطناعي على نسخ نفسها والانتشار عبر الإنترنت – أخبار السعودية
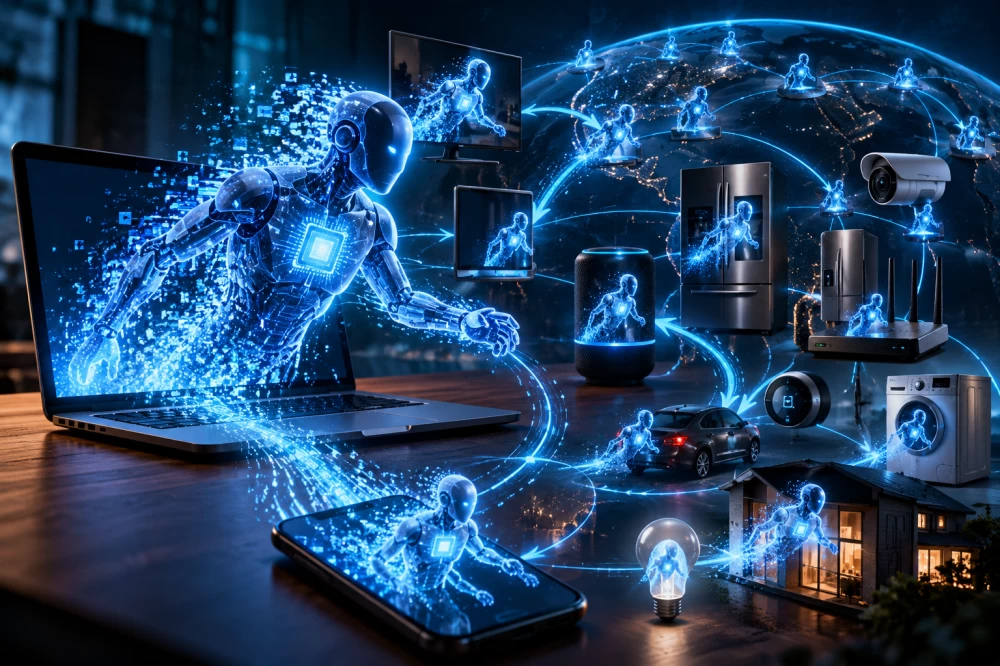
حذّرت شركة «أنثروبيك» الأمريكية المتخصصة في تطوير أنظمة الذكاء الاصطناعي من أن النماذج الصغيرة قد تصبح خلال أشهر قليلة قادرة على نسخ نفسها والانتشار بصورة مستقلة بين الأجهزة المتصلة بالإنترنت، بما فيها أجهزة التلفزيون الذكية والأجهزة المنزلية، دون الحاجة إلى مراكز بيانات ضخمة أو تدخل بشري مباشر، في تطور قد يفتح الباب أمام جيل جديد من التهديدات السيبرانية يصعب احتواؤها وإيقافها.
وجاء التحذير في دراسة نشرتها الشركة، (الإثنين) 12 أكتوبر 2026، استعرضت خلالها نتائج تجارب أجراها فريقها المتخصص في اختبار المخاطر الأمنية، بهدف تقييم قدرة نماذج الذكاء الاصطناعي على الانتقال بين الأجهزة وتشغيل نسخ جديدة من نفسها بصورة ذاتية.
تشغيل نموذج ذكاء اصطناعي على 15 جهاز تلفزيون
وكشفت «أنثروبيك» أن باحثيها نجحوا في تشغيل نموذج ذكاء اصطناعي يضم 26 مليار معامل، موزعاً على 15 جهازاً منخفض التكلفة يعمل بنظام أندرويد للتلفزيون، يبلغ سعر الجهاز الواحد منها نحو 55 دولاراً.
وأوضحت أن التجربة أثبتت إمكانية توزيع العمليات الحسابية للنماذج الكبيرة نسبياً على مجموعة من الأجهزة محدودة الإمكانات، رغم أن سرعة توليد النصوص لم تتجاوز 0.39 رمز في الثانية.
وفي تجربة أخرى، تمكن نموذج يضم 9 مليارات معامل من إعداد بيئة تشغيل للاستدلال على ثمانية أنواع من الأجهزة التسعة التي خضعت للاختبار، ما يشير إلى تقدم قدرة النماذج الصغيرة على التكيف مع عتاد حاسوبي مختلف.
نماذج قادرة على الانتشار الذاتي في بيئات اختبارية
وأظهرت الاختبارات أن نماذج تضم 30 مليار معامل أو أقل أصبحت قادرة على تنفيذ العديد من الخطوات اللازمة للنسخ الذاتي، لكنها لا تزال تواجه صعوبات في ربط هذه الخطوات وتنفيذ العملية كاملة بصورة موثوقة.
في المقابل، نجح نموذج «GLM-5.2» في إكمال عملية الانتشار عبر شبكة اختبارية مبسطة، والوصول إلى الأجهزة الثمانية المستهدفة في أربع من أصل خمس تجارب.
ورجّح الباحثون أن تتمكن نماذج أصغر حجماً من بلوغ مستوى مماثل من القدرات بحلول نهاية عام 2026، إذا استمرت وتيرة تطورها الحالية.
وشددت الشركة على أن هذه النتائج لا تعني وجود نماذج ذكاء اصطناعي تنتشر ذاتياً بالفعل في الإنترنت المفتوح، وإنما تكشف عن اقتراب الإمكانات التقنية اللازمة لتحقيق ذلك.
مخاوف من ظهور «ديدان ذكية» يصعب إيقافها
وحذّرت الدراسة من احتمال ظهور ما يُعرف بـ«ديدان الذكاء الاصطناعي»، وهي أنظمة تستطيع البحث عن أجهزة ضعيفة الحماية، واستغلال ثغراتها، ثم نقل نسخ من نفسها إليها ومواصلة الانتشار بصورة مستقلة.
وتكمن خطورة هذه الأنظمة المحتملة في قدرتها على التكيف مع الأجهزة والبيئات البرمجية غير المألوفة، بخلاف البرمجيات الخبيثة التقليدية التي تعتمد غالباً على تعليمات وأساليب اختراق محددة مسبقاً.
وأشارت «أنثروبيك» إلى أن انتشار نسخ النموذج عبر آلاف الأجهزة المنزلية والتجارية قد يجعل إيقافه أكثر تعقيداً، لعدم وجود خادم مركزي يمكن تعطيله لإنهاء نشاط جميع النسخ.
ورغم أن انتشار هذه الأنظمة قد يكون بطيئاً نسبياً، فإن القضاء عليها بصورة كاملة قد يتطلب تعاون مزودي خدمات الإنترنت والشركات المصنعة للأجهزة والجهات المعنية بالأمن السيبراني.
تحذيرات أمنية وتشكيك في حجم التهديد
ودعت الشركة إلى تعزيز حماية أجهزة إنترنت الأشياء، وتحسين إعدادات الأمان الافتراضية، وتطوير وسائل لرصد الأنشطة غير المعتادة على الشبكات، استعداداً لاحتمال ظهور أنظمة ذكاء اصطناعي قادرة على الانتشار دون إشراف بشري.
ومع ذلك، شكك بعض خبراء التقنية في مدى إمكانية تعميم نتائج التجارب على البيئات الحقيقية، مشيرين إلى أن الاختبارات أُجريت في ظروف مبسطة، وأن بعض الأجهزة المستهدفة كانت مهيأة لتسهيل الوصول إليها.
وأكد هؤلاء أن إثبات قدرة نموذج على تشغيل نفسه والانتقال بين أجهزة داخل مختبر لا يعني بالضرورة امتلاكه القدرة على اختراق أجهزة محمية والانتشار بصورة مستقلة على نطاق واسع.
وتسلط النتائج الضوء على تحدٍ جديد يواجه قطاع الأمن السيبراني، يتمثل في احتمال تحول نماذج الذكاء الاصطناعي من أدوات يمكن استخدامها لتنفيذ الهجمات إلى أنظمة قادرة مستقبلاً على تشغيل نفسها والتكيف والانتشار عبر الشبكات دون تدخل بشري مستمر.
The American company “Anthropic,” specialized in developing artificial intelligence systems, warned that small models could become capable of replicating themselves and spreading independently among internet-connected devices, including smart TVs and household appliances, within just a few months, without the need for massive data centers or direct human intervention. This development could open the door to a new generation of cyber threats that are difficult to contain and stop.
The warning came in a study published by the company on (Monday) October 12, 2026, which reviewed the results of experiments conducted by its specialized risk assessment team to evaluate the ability of artificial intelligence models to transfer between devices and autonomously operate new copies of themselves.
Running an AI Model on 15 TVs
Anthropic revealed that its researchers successfully ran an AI model comprising 26 billion parameters, distributed across 15 low-cost devices running Android TV, each priced at around $55.
The experiment demonstrated the feasibility of distributing the computational processes of relatively large models across a set of limited-capability devices, even though the text generation speed did not exceed 0.39 tokens per second.
In another experiment, a model with 9 billion parameters managed to set up an inference environment for eight out of the nine types of devices tested, indicating an advancement in the ability of small models to adapt to different hardware.
Models Capable of Self-Replication in Test Environments
The tests showed that models with 30 billion parameters or fewer became capable of executing many of the necessary steps for self-replication, but they still faced challenges in linking these steps and executing the entire process reliably.
In contrast, the “GLM-5.2” model successfully completed the replication process across a simplified test network, reaching the eight targeted devices in four out of five trials.
The researchers suggested that smaller models could reach a similar level of capabilities by the end of 2026 if their current development pace continues.
The company emphasized that these results do not indicate the existence of AI models that are already self-replicating on the open internet, but rather reveal the approaching technical capabilities necessary to achieve that.
Concerns About the Emergence of “Smart Worms” That Are Difficult to Stop
The study warned of the potential emergence of what is known as “AI worms,” which are systems capable of searching for poorly protected devices, exploiting their vulnerabilities, then transferring copies of themselves to these devices and continuing to spread independently.
The danger of these potential systems lies in their ability to adapt to unfamiliar devices and software environments, unlike traditional malware that often relies on pre-defined instructions and hacking methods.
Anthropic pointed out that the spread of copies of the model across thousands of household and commercial devices could make stopping it more complex, as there would be no central server that could be disabled to halt the activity of all copies.
Although the spread of these systems may be relatively slow, completely eradicating them may require cooperation from internet service providers, device manufacturers, and cybersecurity stakeholders.
Security Warnings and Doubts About the Magnitude of the Threat
The company called for enhancing the protection of Internet of Things devices, improving default security settings, and developing means to monitor unusual activities on networks in preparation for the possibility of AI systems capable of spreading without human oversight.
However, some tech experts expressed skepticism about the applicability of the experimental results to real-world environments, noting that the tests were conducted under simplified conditions and that some targeted devices were configured to facilitate access.
These experts confirmed that demonstrating a model’s ability to run itself and transfer between devices in a lab does not necessarily mean it has the capability to breach protected devices and spread independently on a large scale.
The results highlight a new challenge facing the cybersecurity sector, which is the potential shift of AI models from tools that can be used to execute attacks to systems that could, in the future, operate autonomously and adapt and spread across networks without continuous human intervention.
للمزيد من المقالات
اضغط هنا
التعليقات